Certification
ISO 27001 and ISO 9001 certified.
Independently audited information security and quality management, so your data, your project and your customers are in safe hands. Both are demanding standards to achieve, and to keep.
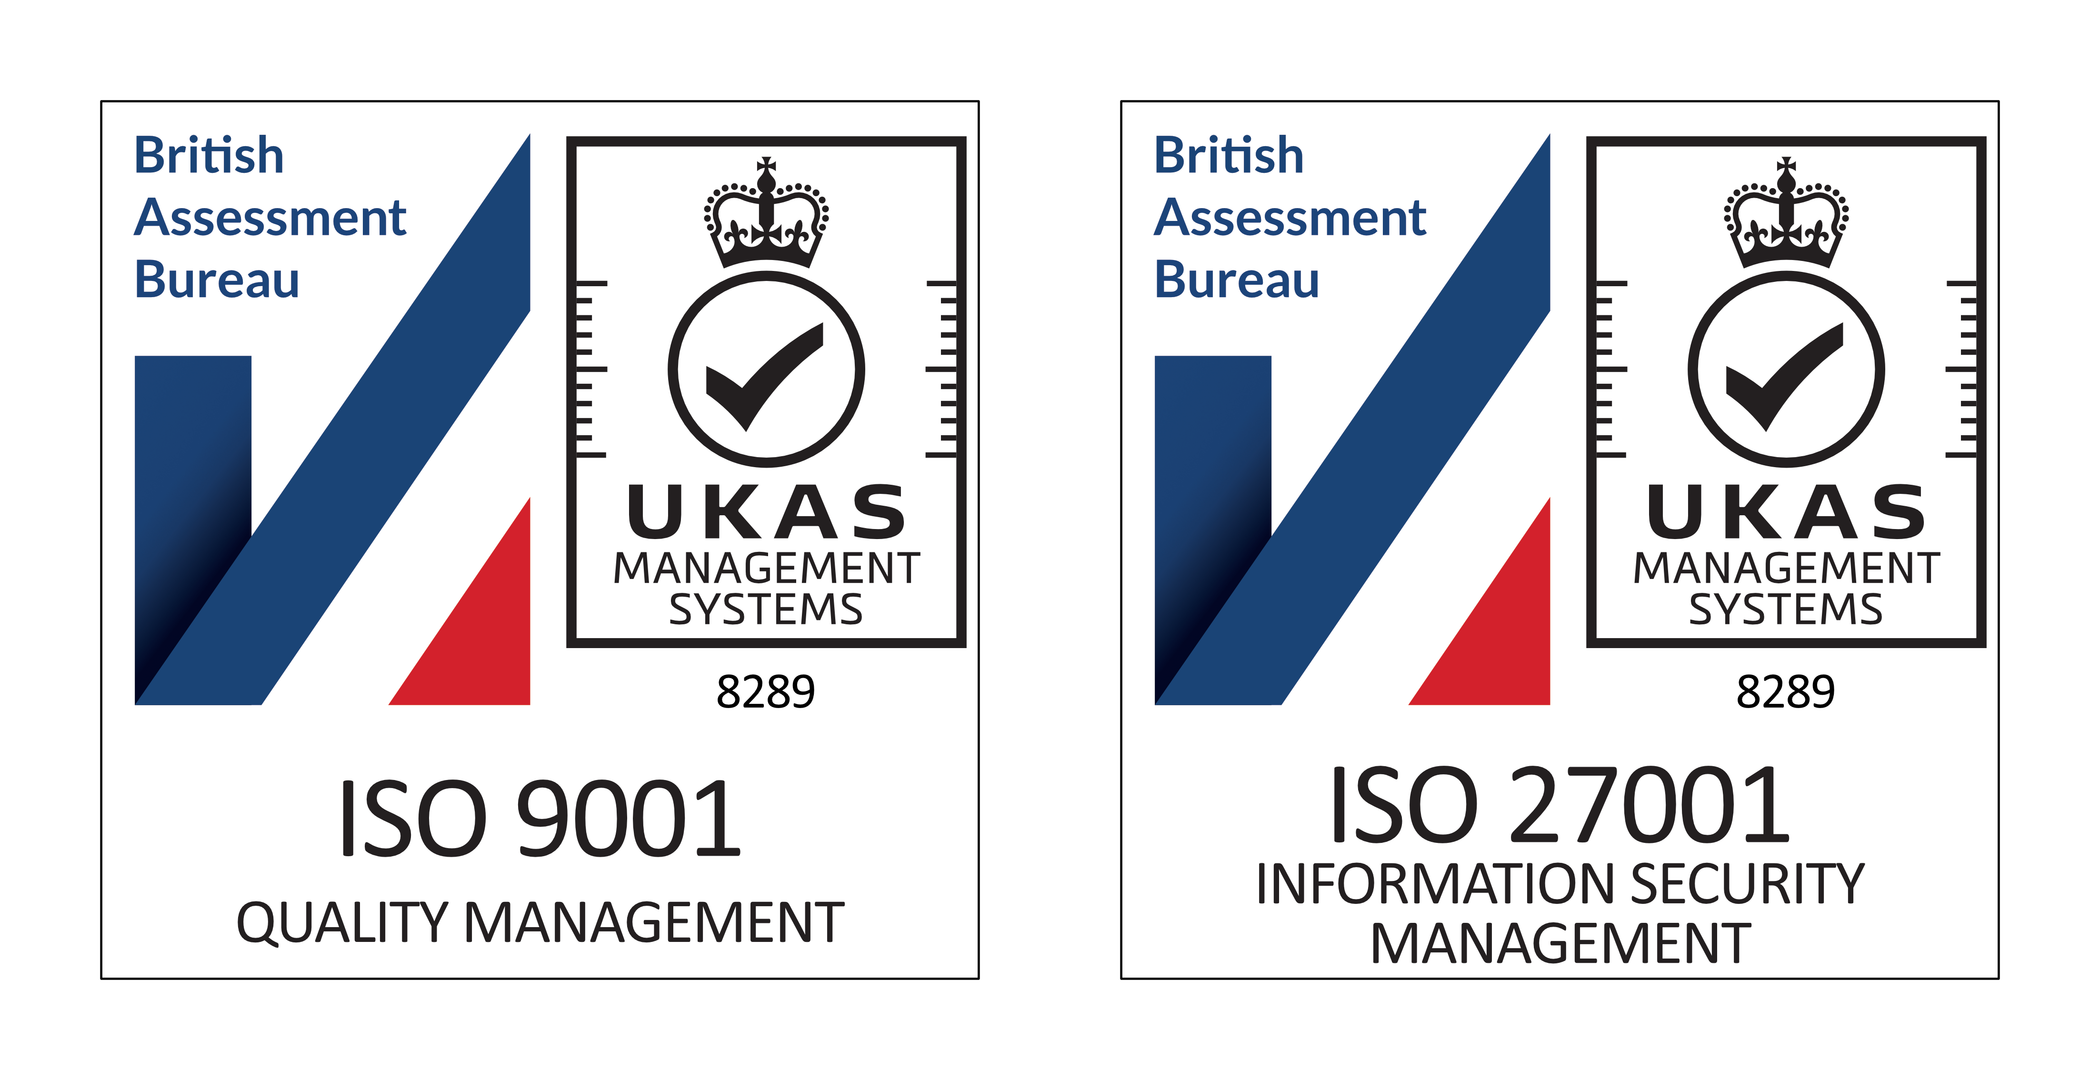
Two standards, independently audited.
ISO/IEC 27001:2022
Information security · certificate 239491
The leading international standard for information security management. It protects the confidentiality, integrity and availability of information, yours and ours.
ISO 9001:2015
Quality management · certificate 206025
The international standard for quality management systems: documented processes, clear responsibilities and continual improvement in everything we deliver.
What information security certification means.
ISO 27001 is published jointly by the International Organization for Standardization and the International Electrotechnical Commission. It sets the requirements for an information security management system (ISMS), built around three objectives: confidentiality, integrity and availability.
To be certified, an organisation has to:
- identify what its stakeholders expect of its information security
- identify the risks to its information
- define controls to meet those expectations and handle those risks
- set clear information security objectives
- put the controls and risk treatments in place
- measure how well they work, and keep improving the system
There are many clauses and specific requirements, and the certification process is complex and lengthy, which is what makes ISO 27001 one of the hardest certifications to achieve.
What quality management certification means.
ISO 9001 sets the requirements for a quality management system (QMS): a formal system that documents the processes, procedures and responsibilities for meeting quality objectives. It is built on principles including customer focus, leadership, engagement of people, the process approach, continual improvement and evidence-based decision making.
Certification shows that we have created, implemented and maintain a quality management system that meets the standard, and that an independent auditor has checked it.
What our certification gives our clients.
Your data, protected
Customer records, orders, pricing and system access are handled under audited security controls, including the data our AI work touches.
Consistent delivery
Projects run on documented, audited processes, so quality doesn't depend on who happens to be working on them.
Easier procurement
Many supplier questionnaires and tenders ask for ISO 27001 and ISO 9001. With our certificates, much of that due diligence is already done.
Always improving
Both standards require regular internal audits, management reviews and external surveillance audits, so the systems keep getting better rather than standing still.
Verify our certificates.
You can verify the validity of our ISO certificates via this link: certcheck.ukas.com.
- ISO/IEC 27001:2022, certificate 239491: download the certificate (PDF)
- ISO 9001:2015, certificate 206025: download the certificate (PDF)
Read our announcement: PureNet receives ISO 27001 and ISO 9001 accreditation.
What our certification covers.
Both certificates cover the same scope, word for word from the certificates:
The provision of ecommerce and portal solutions encompassing bespoke portals, system integration, AI app development, web design, consultancy and support for B2C and B2B businesses throughout the UK.
Our information security and quality management systems run as one business management system, covering all our people, processes and services within that scope.
Working towards ISO 42001 for AI.
ISO/IEC 42001 is the first international standard for managing artificial intelligence responsibly. We're working towards it, building AI governance into the ISO 27001 and ISO 9001 management system we already run, across all our brands.
It will cover the AI agents we design and deliver for clients, the AI features in our products, and the AI we use ourselves in sales, support, engineering and the search on this website. Our approach builds on GOVERN: From AI Risk to Responsible Advantage, the practical guide to governing AI in business written by our Group CEO, Dr Paul M. Gibson, and published by Enceladus AI, part of the PureNet Group. Its central idea is to govern the use of AI, not the technology.
What it will mean for our clients:
- Assurance you can check. How we design, test, deploy and monitor AI will be independently audited, as our information security and quality already are.
- Clear responsibilities. Who is responsible for what, between us, our AI suppliers and you, is set out for every system we build or run.
- Easier procurement. A recognised answer to the AI governance questions now appearing in tenders and supplier questionnaires.
- Ready for regulation. A structured way to meet emerging AI rules, including the EU AI Act where it applies.
We're not yet certified to ISO 42001. We'll update this page as we progress. To see how we help clients govern their own AI, see AI governance and assurance.
Our policies, in one place.
For auditors, procurement teams and anyone who wants to check how we work.
Quality policy
ISO 9001
Our commitments to clients, suppliers and our team, signed by the board.
Information security policy
ISO 27001
How we protect the confidentiality, integrity and availability of information.
Secure development and OWASP
ISO 27001
The OWASP Top 10 for web and AI applications, and how our secure development controls apply them.
Business continuity
ISO 27001
How we plan for disruption and keep clients' hosted services running.
Reporting a security issue
Vulnerability disclosure
Found a vulnerability in something we run? How to tell us, and what we'll do.
Feedback and complaints
ISO 9001
How to give us feedback or make a complaint, and what happens next.
Privacy policy
UK GDPR
How we handle personal information, including our role as a data processor for clients.
Sub-processors
UK GDPR
The service providers we use when we process personal data for our clients, and where.
Cookie policy
Cookies
The cookies this website uses, and how to change your choice.
Environmental policy
Environment
How we measure and reduce our impact on the environment.
ESG statement
Responsible business
Our environmental, social and governance responsibilities, in one place.
Carbon reduction plan
Net zero by 2040
Our emissions, our reduction targets and our path to net zero.
Modern slavery statement
Responsible business
The steps we take against modern slavery and human trafficking.
Health and safety policy
Responsible business
How we keep our people and others safe across the PureNet Group.
Accessibility statement
WCAG 2.2 AA
How we make this website usable for everyone, how we test it, and how to report a problem.
Website terms of use
Legal
The terms for using this website.